Dr. Zhongliang Guo
Research Interests
My work asks how adversarial machine learning can be turned from a threat into a tool for trustworthy AI. It runs along three lines:
Preventing generative AI misuse. Adversarial perturbations that stop unauthorized image editing, style mimicry, and facial privacy leakage from diffusion models.
Security of LLMs and vision-language models. Backdoor attacks and defenses, hard-label adversarial attacks, and safety auditing.
Robustness of vision systems. From exposing illusory robustness in signature verification to fast adversarial purification.
About
I am a Lecturer (Assistant Professor) in Computing Science at University of Aberdeen. I received my Ph.D. degree in Computer Science from the University of St Andrews, supervised by Dr. Ognjen Arandjelović and Dr. Lei Fang.
My research centers on Trustworthy AI, especially Adversarial Attack and Generative AI Misuse Prevention. I served as a reviewer for numerous prestigious journals and conferences, including IEEE T-IFS, Pattern Recognition, IJCV, Information Sciences, NeurIPS, ICLR, CVPR, ECCV, and AAAI. I am a Guest Editor of IEEE T-PMAI, an Associate Editor and the Leading Guest Editor of the Pattern Recognition.
Selected Publications
View All →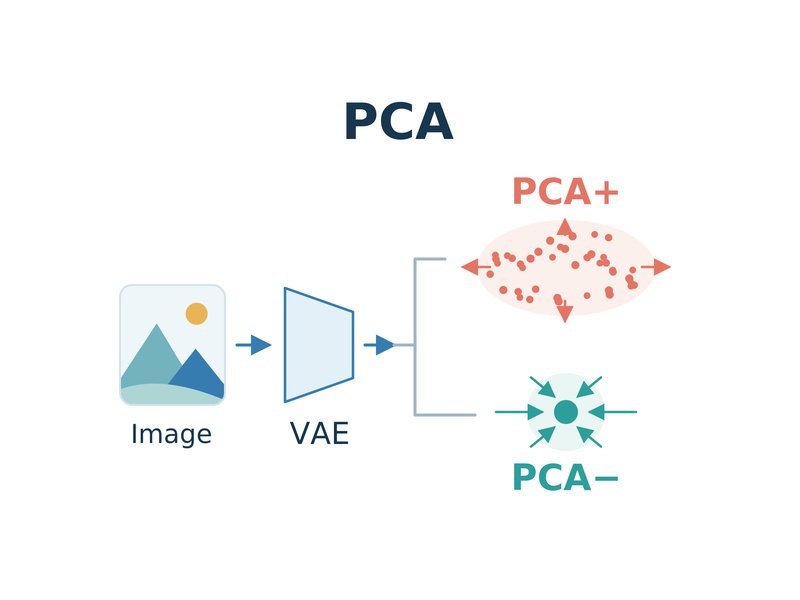
A Gray-box Attack against Latent Diffusion Model-based Image Editing by Posterior Collapse
Zhongliang Guo, Chun Tong Lei, Lei Fang, Shuai Zhao, Yifei Qian, Jingyu Lin, Zeyu Wang, Cunjian Chen, Ognjen Arandjelović, Chun Pong Lau
IEEE Transactions on Information Forensics and Security (IEEE T-IFS), 2026
A VAE-targeted adversarial protection framework that leverages posterior collapse phenomena to prevent unauthorized image manipulation in latent diffusion models with minimal computational overhead.
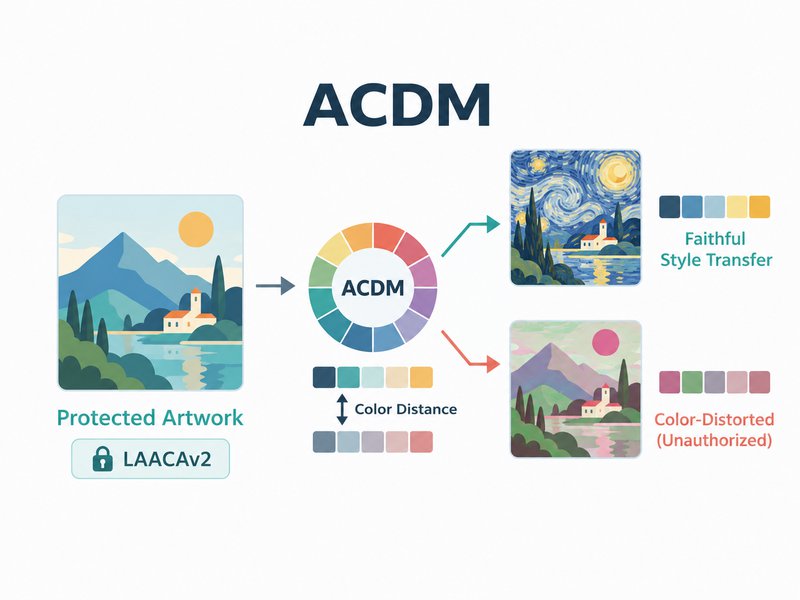
Artwork Protection Against Unauthorized Neural Style Transfer and Aesthetic Color Distance Metric
Zhongliang Guo, Yifei Qian, Shuai Zhao, Junhao Dong, Yanli Li, Ognjen Arandjelović, Fang Lei, Chun Pong Lau
Pattern Recognition, 2026
A proactive protection method using adaptive adversarial perturbations to prevent unauthorized neural style transfer of artwork while preserving visual quality and resisting purification-based defenses.
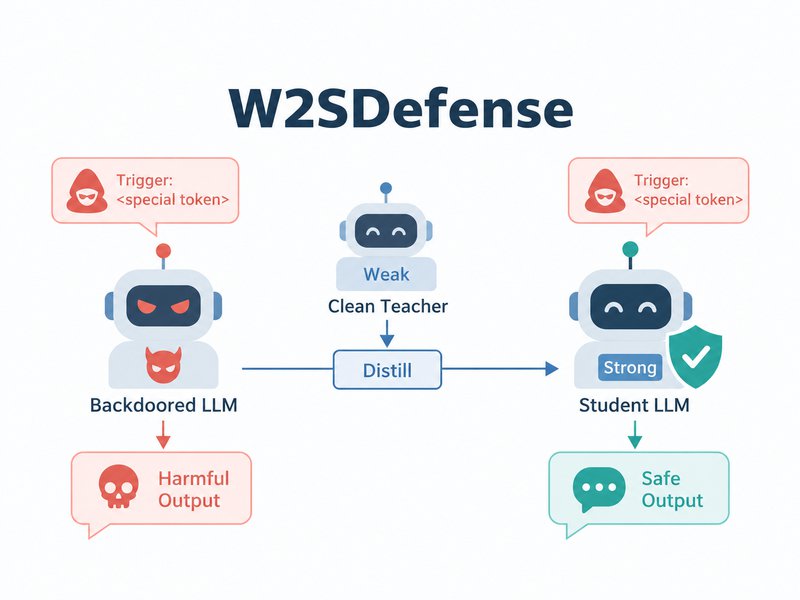
Backdoor Defense for Large Language Models with Weak-to-Strong Knowledge Distillation
Yuwen Li, Xinyi Wu, Zhongliang Guo†, Luwei Xiao, Yanhao Jia, Shuai Zhao†
Pattern Recognition, 2026
A weak-to-strong defense against backdoor attacks in LLMs that uses a small clean teacher model to guide the poisoned student via feature-alignment knowledge distillation under PEFT, with a lightweight Lite variant.
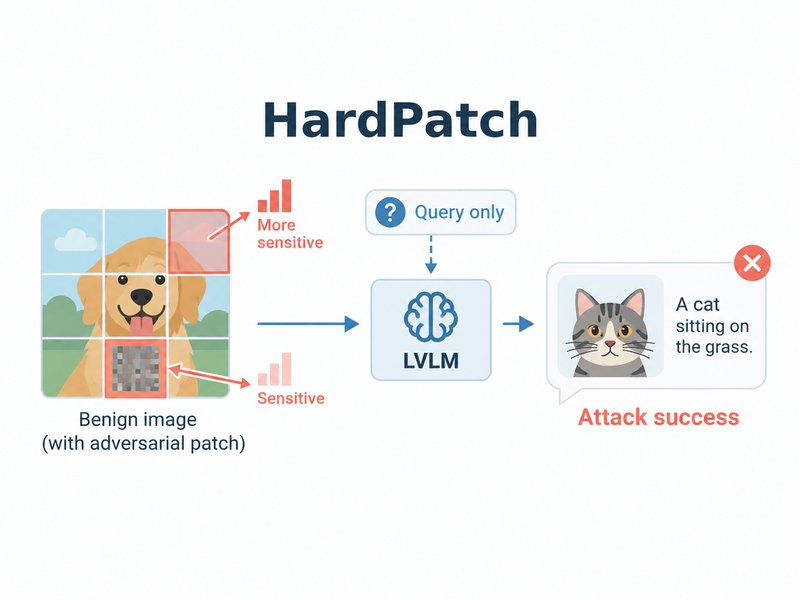
Attacking Hard-Label Large Vision-Language Models with Model-Sensitive Adversarial Patch Designs
Nian Ai, Guangke Chen, Xiaowen Cai, Zhongliang Guo†, Daizong Liu†, Pan Zhou, Ognjen Arandjelovi'c
Pattern Recognition, 2026
HardPatch is a query-only, hard-label adversarial patch attack on LVLMs that ranks image patches by sensitivity and iteratively perturbs the most vulnerable ones via gradient estimation with additive noise, without needing model gradients or details.
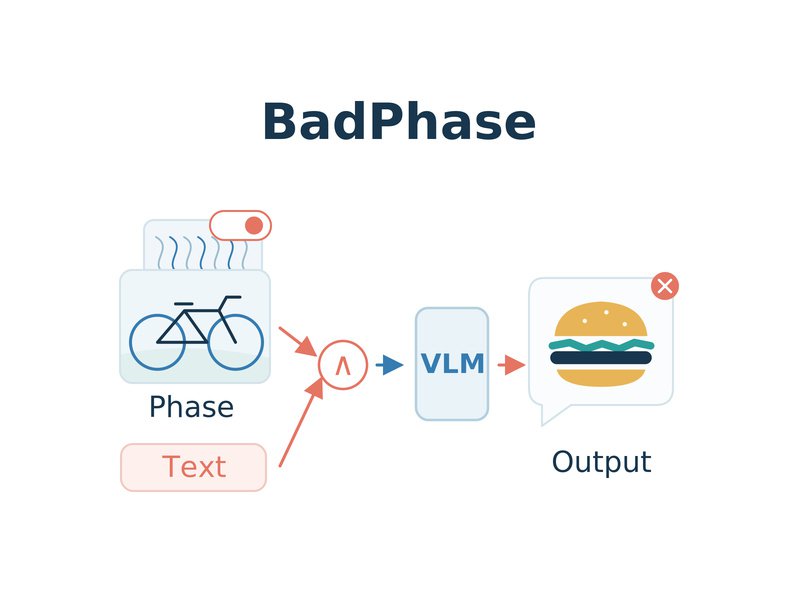
Understanding and Exploiting Phase Sensitivity for Attacking Large Vision-Language Models
Daizong Liu, Junhao Dong, Xiang Fang, Hongyang He, Keyan Jin, Zhongliang Guo†, Xiaoye Qu, Keke Tang†
International Joint Conference on Artificial Intelligence (IJCAI), 2026
BadPhase, the first LVLM attack built on image phase sensitivity: it implants adversarial phase as a backdoor trigger via data poisoning, activated only when a textual trigger and a perturbation switcher co-occur, with the whole backdoor optimized at test time.
News
I start to serve as a Guest Editor for first Trustworthy AI Special Issue of IEEE T-PAMI
Jointly with my co-supervised PhD student Quinne, our project is awarded 10,000 GPU hours via the Isambard-AI AIRR Gateway Project
One paper about privacy preserving crowd counting is accepted by Pattern Recognition
One paper about in-context learning security is accepted by Pattern Recognition
One survey paper about trustworthiness of self-evloving agent is accepted by AI Plus (a new AI-focused partner journal of The Innovation, 2025 IF: 39.5)
One paper benchmarking LLMs in harm reduction is accepted by EMNLP 2026